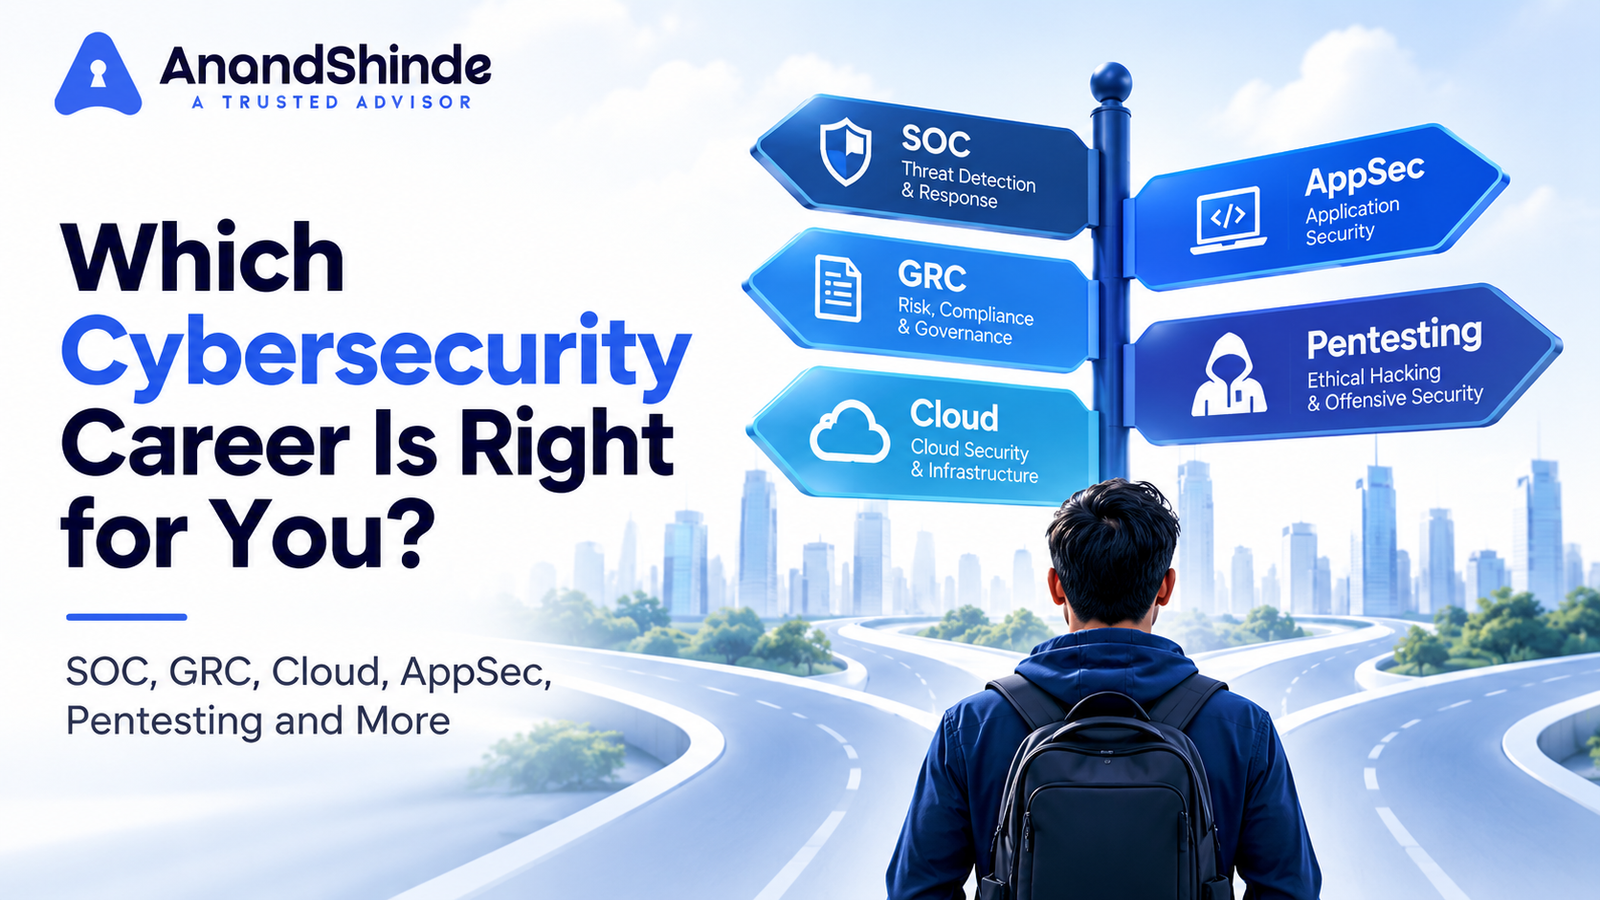
Cybersecurity is often described as though it were one career. In reality, it contains many very different career paths.
One professional may spend the day investigating suspicious activity. Another may assess business risk and regulatory requirements. Someone else may secure cloud infrastructure, review application vulnerabilities or ethically attack systems to discover weaknesses before criminals do.
That is why asking “How do I get into cybersecurity?” is only the beginning.
A better question is:
Which cybersecurity career matches the way I naturally like to think, solve problems and work?
SOC and Security Operations: If You Enjoy Investigation
A Security Operations Centre, or SOC, can be a strong fit for people who enjoy investigation and problem-solving.
SOC analysts monitor security alerts, review logs, investigate suspicious behaviour and determine whether an event represents a genuine threat.
As experience grows, the career can lead toward threat hunting, detection engineering, malware analysis or incident response.
You may enjoy SOC work if you like asking:
What happened, how did it happen and what should we do next?
Networking, operating systems, SIEM tools and log analysis are particularly valuable skills in this path.
GRC: If You Like Risk, Business and Communication
Governance, Risk and Compliance—commonly called GRC—is very different from the popular image of cybersecurity as hacking.
GRC professionals help organizations understand security risks, develop policies, assess controls, prepare for audits and meet regulatory or contractual requirements.
This career often suits people who enjoy structured thinking, documentation, communication and working with both technical and business stakeholders.
You do not need to spend every day writing code to have a successful cybersecurity career.
If you can understand technical risk and explain its business impact clearly, GRC can be an excellent direction.
Cloud Security: If Infrastructure Interests You
Modern organizations increasingly depend on platforms such as Microsoft Azure, AWS and Google Cloud.
Cloud security professionals help protect those environments through identity management, network controls, encryption, logging, secure configuration and monitoring.
This path can be particularly suitable for people coming from system administration, networking, infrastructure or DevOps backgrounds.
Cloud security is not simply about learning where buttons are located inside one cloud platform. Strong professionals understand architecture and know how to design secure systems rather than only respond when something goes wrong.
Application Security: If You Like Software and Security
Application Security, or AppSec, sits between cybersecurity and software development.
AppSec professionals work with developers to identify and prevent vulnerabilities throughout the software development lifecycle.
Their work may involve secure code review, threat modelling, SAST, SCA, DAST, vulnerability triage and secure development practices.
If you enjoy understanding how applications are built and want to prevent security problems before software reaches production, AppSec may suit you.
You do not necessarily need to become a full-time software developer, but understanding programming concepts and development processes is extremely valuable.
Penetration Testing: If You Enjoy Breaking Things—Legally
Penetration testing is one of cybersecurity’s most visible career paths.
Pentesters simulate real attacks against networks, applications and systems to identify vulnerabilities and demonstrate their potential impact.
This path suits curious people who enjoy hands-on technical work, web technologies, networking, scripting and experimentation.
However, professional penetration testing involves much more than “hacking.”
You also need methodology, ethics, documentation and the ability to explain vulnerabilities clearly enough that another team can remediate them.
Incident Response and Digital Forensics: If You Need to Know What Happened
Incident responders become essential when preventive controls fail.
They investigate compromised environments, identify what attackers did, contain incidents and help organizations recover.
Digital forensics goes deeper into devices, logs, files and other artefacts to reconstruct activity.
If SOC work appeals to you but you want deeper investigations, incident response or digital forensics may be worth exploring.
Security Engineering and IAM: If You Prefer Building Security
Not everyone wants to investigate alerts or attack systems.
Security engineers design and implement controls across networks, endpoints, cloud platforms and enterprise environments.
Identity and Access Management specialists focus on authentication, authorization, privileged access, single sign-on and user lifecycle management.
These careers often suit people who enjoy architecture, automation and building reliable systems.
So Which Cybersecurity Path Should You Choose?
Do not choose your cybersecurity specialization simply because it is trending or because somebody says it has the highest salary.
Consider how you naturally work.
If you enjoy investigation, explore SOC, threat hunting or incident response.
If you enjoy business, risk and communication, consider GRC.
If infrastructure interests you, explore cloud security or security engineering.
If you enjoy software, investigate AppSec.
If you enjoy offensive technical problem-solving, explore penetration testing.
And remember: your first cybersecurity specialization does not have to become your permanent career.
Build a Career Path, Not a Certification Collection
Once you know which direction you want to pursue, choosing your learning path becomes much easier.
Instead of collecting unrelated certifications, you can select qualifications, practical labs, projects and technical skills that support your target role.
That is where structured career planning becomes valuable.
At AnandShinde.com, Career Counselling focuses on understanding your existing experience, strengths, interests, skills gaps and long-term goals before creating a practical career-development roadmap.
Cybersecurity offers many exciting paths.
The objective is not to choose the one that sounds most impressive.
It is to find the cybersecurity career where your strengths, interests and working style give you the strongest opportunity to succeed and grow.
Have knowledge, experience, or a powerful idea you want to turn into a book? Get your book published with DevOM Publishing:
https://www.devompublishing.com/
If your business needs cybersecurity services, AI security guidance, cloud security review, or protection against modern cyber threats, visit DevOM Consulting:
https://devomconsulting.com/