Sweden’s decision to restrict public access to ChatGPT and Claude on government-managed computers has attracted attention across the technology and cybersecurity community.
But the story is more nuanced than a simple “AI ban.”
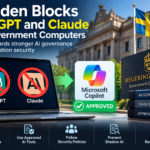
From October 26, 2026, employees within Sweden’s Government Offices are being prevented from directly accessing the public versions of ChatGPT and Claude from official work computers.
The restriction does not apply to Swedish citizens or private businesses.
Instead, it reflects a growing enterprise concern: how can organizations benefit from generative AI without allowing sensitive information to flow into tools that have not been formally reviewed, governed, or approved?
For businesses, this may be the more important part of the story.
Why Sweden Took Action
The main concern behind the restriction is information security.
Generative AI tools have become part of everyday work remarkably quickly. Employees use them to summarize documents, improve writing, analyze information, generate code, prepare presentations, and accelerate research.
Those productivity benefits are significant.
The problem begins when employees enter information into external AI platforms without understanding how that information is handled.
Government or corporate users might unintentionally submit:
- Confidential documents
- Internal business information
- Source code
- Customer or employee data
- Security findings
- Legal material
- Strategic plans
- Credentials or technical configurations
Once sensitive information leaves an organization’s controlled environment, questions arise around retention, privacy, contractual protections, access, monitoring, and data processing.
That is the risk Sweden is trying to manage.
This Is Really a Shadow AI Problem
The situation closely resembles the challenge organizations previously faced with Shadow IT.
Employees discover a useful technology and begin using it before security, legal, privacy, procurement, or compliance teams have reviewed it.
With generative AI, this has created a newer problem:
Shadow AI.
An employee may have no malicious intention. They may simply want to complete a task faster.
But from the organization’s perspective, an unapproved AI tool can become another uncontrolled data-processing environment.
The issue is therefore not whether AI is useful.
It clearly is.
The issue is whether the organization understands where its information is going and under what conditions.
Why Microsoft Copilot Is Still Allowed
One of the most important details in Sweden’s approach is that government employees are not being told to stop using AI entirely.
They are reportedly being directed toward approved alternatives such as Microsoft Copilot, where security settings and organizational controls have been reviewed.
That distinction matters.
It would be incorrect to conclude that Sweden considers one AI model inherently safe and another inherently dangerous.
The real difference is the governance framework around the service.
Enterprise AI deployments can include stronger controls around authentication, administration, contractual data protections, monitoring, access management, and organizational policy.
Reports also indicate that some government users may still access ChatGPT and Claude models through internally governed AI environments.
That highlights the central principle:
The model itself is only one part of AI security. The environment in which it is accessed matters just as much.
What Enterprises Should Learn From This
Organizations should assume that employees are already experimenting with generative AI.
Simply ignoring the issue does not prevent it.
A stronger approach is to define what acceptable AI usage looks like.
Every organization should be able to answer questions such as:
Which AI tools are approved?
What information can employees enter into them?
What information is prohibited?
Who evaluates new AI platforms?
How are users authenticated?
Can activity be logged and monitored?
What happens if sensitive information is accidentally submitted?
Without clear answers, employees are left to make security decisions themselves.
That is rarely an effective governance strategy.
Build an Approved AI Framework
A practical enterprise AI programme should combine several controls.
Data classification should define which categories of information may or may not be entered into external AI services.
Approved-tool lists should identify platforms that have passed security, privacy, legal, and procurement reviews.
Identity and access controls should ensure enterprise AI services use appropriate authentication and authorization.
Monitoring and logging should provide visibility into how approved platforms are being used.
Employee education should include practical examples of safe and unsafe AI usage rather than vague warnings.
Vendor assessment should consider data retention, subprocessors, model training, geographic data handling, and contractual commitments.
These controls allow organizations to enable AI while maintaining accountability.
Why Simply Banning AI Can Create More Risk
There is also a danger in taking an overly restrictive approach.
Employees use generative AI because it saves time.
If organizations block every useful tool without providing approved alternatives, staff may begin using personal accounts, private devices, browser extensions, or other unsanctioned services.
That reduces organizational visibility even further.
A stronger strategy is therefore:
Provide safe alternatives while restricting uncontrolled ones.
That appears to be the direction reflected in Sweden’s approach.
AI Governance Is Becoming Part of Cybersecurity
Generative AI is rapidly becoming another layer of enterprise technology.
Organizations already apply governance to cloud platforms, email systems, SaaS applications, endpoints, identities, and privileged access.
AI now requires similar discipline.
The question for enterprises is no longer simply:
“Should our employees use AI?”
For many organizations, that question has already been answered by employee behavior.
The more useful questions are:
Which AI tools should they use? What data can they share? What controls must be applied? And who is responsible for managing the risk?
Sweden’s decision illustrates an important shift in enterprise security thinking.
The future is unlikely to be about choosing between AI adoption and AI security.
It will be about doing both.
Organizations that govern AI well will be better positioned to gain its productivity benefits without losing control of their information.
Have knowledge, experience, or a powerful idea you want to turn into a book? Get your book published with DevOM Publishing:
https://www.devompublishing.com/
If your business needs cybersecurity services, AI security guidance, cloud security review, or protection against modern cyber threats, visit DevOM Consulting:
https://devomconsulting.com/